Wallet sign-in update in MineBench: a server-issued single-use nonce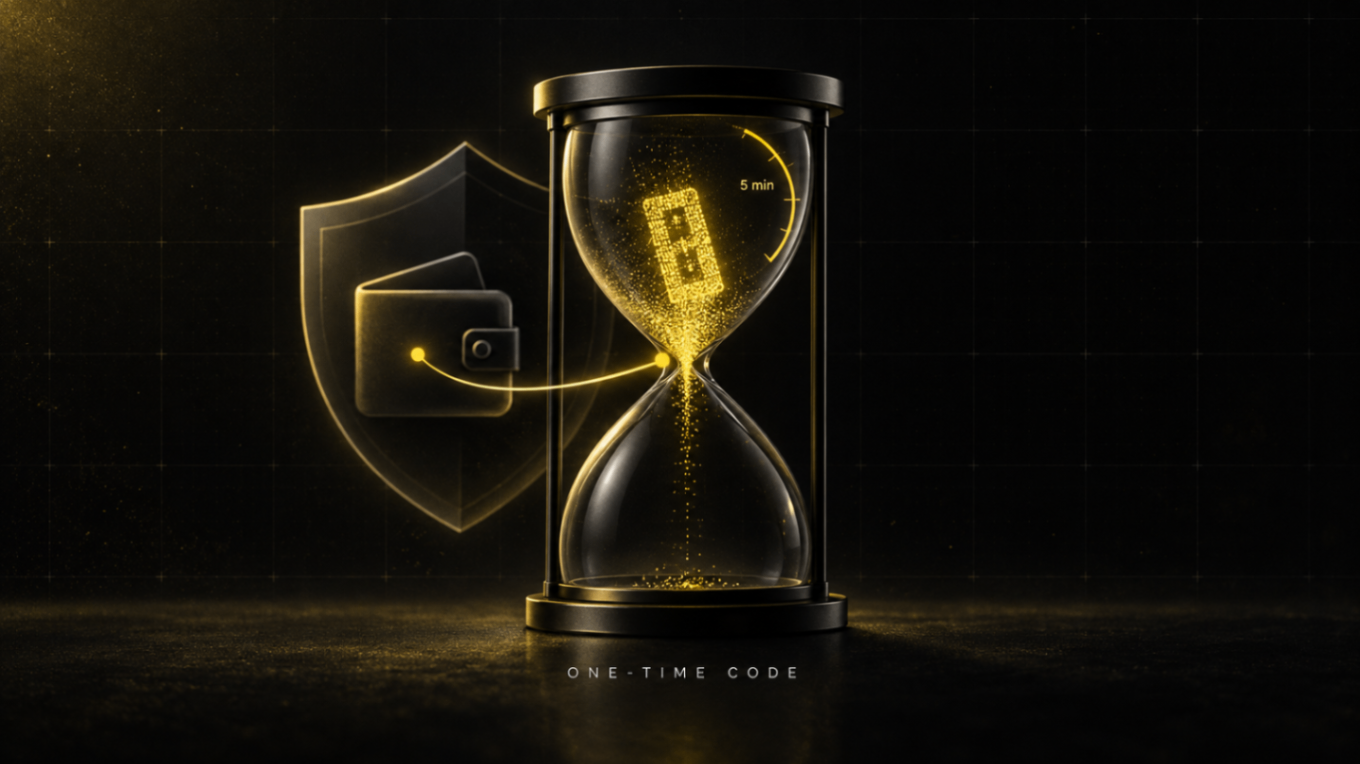
MineBench has updated wallet sign-in: it now uses a server-issued single-use nonce. The wallet here is tied directly to mining rewards and payouts, so this sign-in is protected without compromise. In the first version of the flow we verified a wallet signature over a message the client supplied. That proves key ownership, but it leaves a gap: if that signed message is ever captured, it can be presented again to authenticate as the same wallet. For a dApp that tracks earnings, a replayable login approval was not something we were willing to ship.
How it works now:
The backend issues a random nonce, bound to the wallet address and our domain, and stores the exact message to sign server-side.
The nonce expires after 5 minutes, and the client never chooses the signed text.
On login we verify the signature and atomically consume the nonce in Postgres before any session is issued — a used, expired, or missing nonce is rejected outright.
Sign-in signs a short text message, never a transaction: no keys, no funds, fully self-custodial.
Paired with server-side session revocation (a per-user session version), so logouts and bans invalidate live tokens.
The result: a login approval can't be replayed or reused, which matters precisely because these sessions gate reward attribution and payouts. The same update expands wallet support to Phantom, Solflare, Backpack, Glow, Magic Eden and other Wallet Standard wallets.
Building MineBench at the Colosseum hackathon.
Give feedback to the team
Your message is private to you and the MineBench team.
Create an account to send feedbackAfter signup, you can write a private message with this update attached.