What changed after we talked consent receipts through with a lawyer
This week we sat down with a lawyer to talk consent receipts through, and afterwards we made three decisions:
It stays open. We’ve decided not to seek a patent on consent receipts. The prototype stays open source, and its commit history is our dated record of the work.
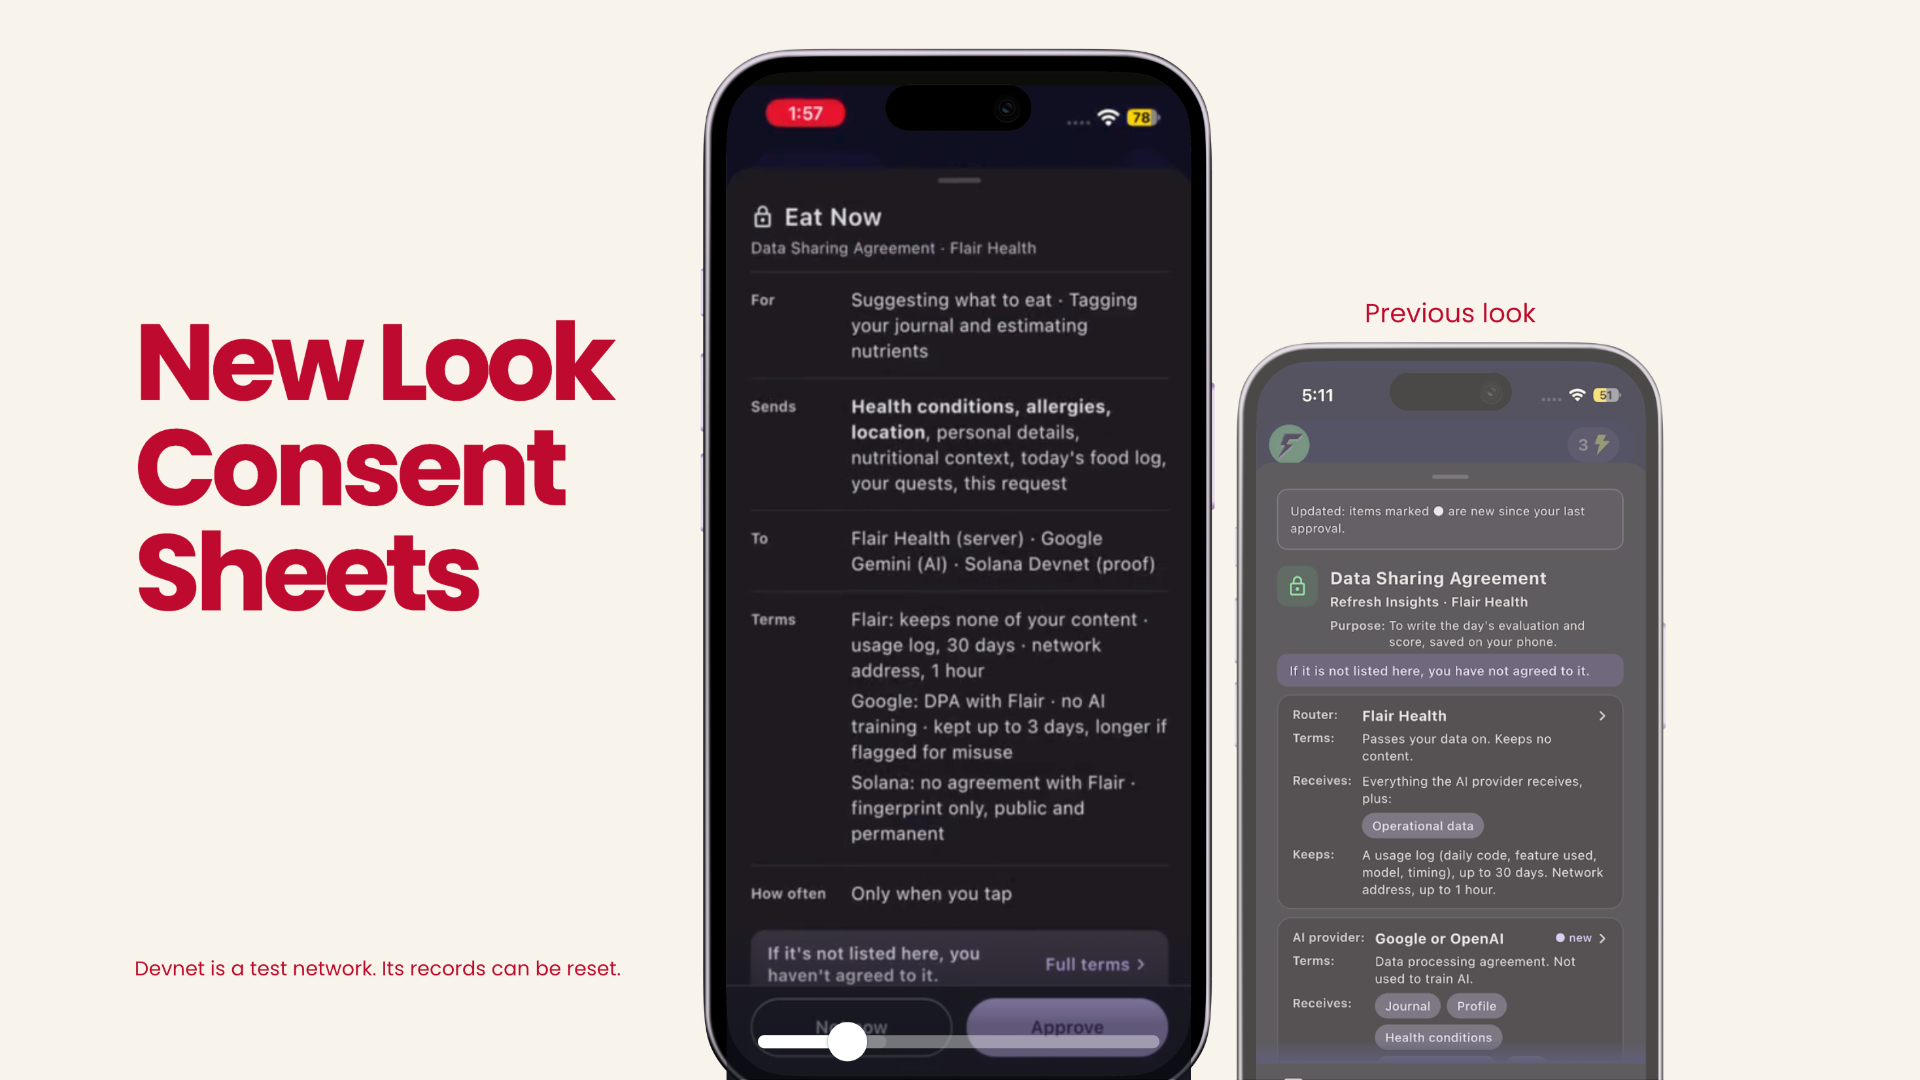
The agreement gets shorter. People skip whatever stands between them and what they came to do, and our agreement screen had grown to read like fine print. We’re designing a short version: what is sent, to whom, what is kept and on what terms, one line each, with the full terms one tap away and the receipt tied to them.
Both sides should sign. A record is stronger when both sides sign it and an independent clock dates all of it. Today the phone signs its receipts, and in our internal build two features also put their receipts’ fingerprints on Solana’s devnet, its test network, which dates their contents. Three gaps remain: the date doesn’t yet cover the signature, the phone’s key isn’t tied to a person, and Flair doesn’t yet countersign. The first and last are on our list; the second has to be solved without asking you for an account.
We also narrowed a line in our docs: the fingerprint contains none of your information, though the ledger shows that Flair recorded a receipt, and when.
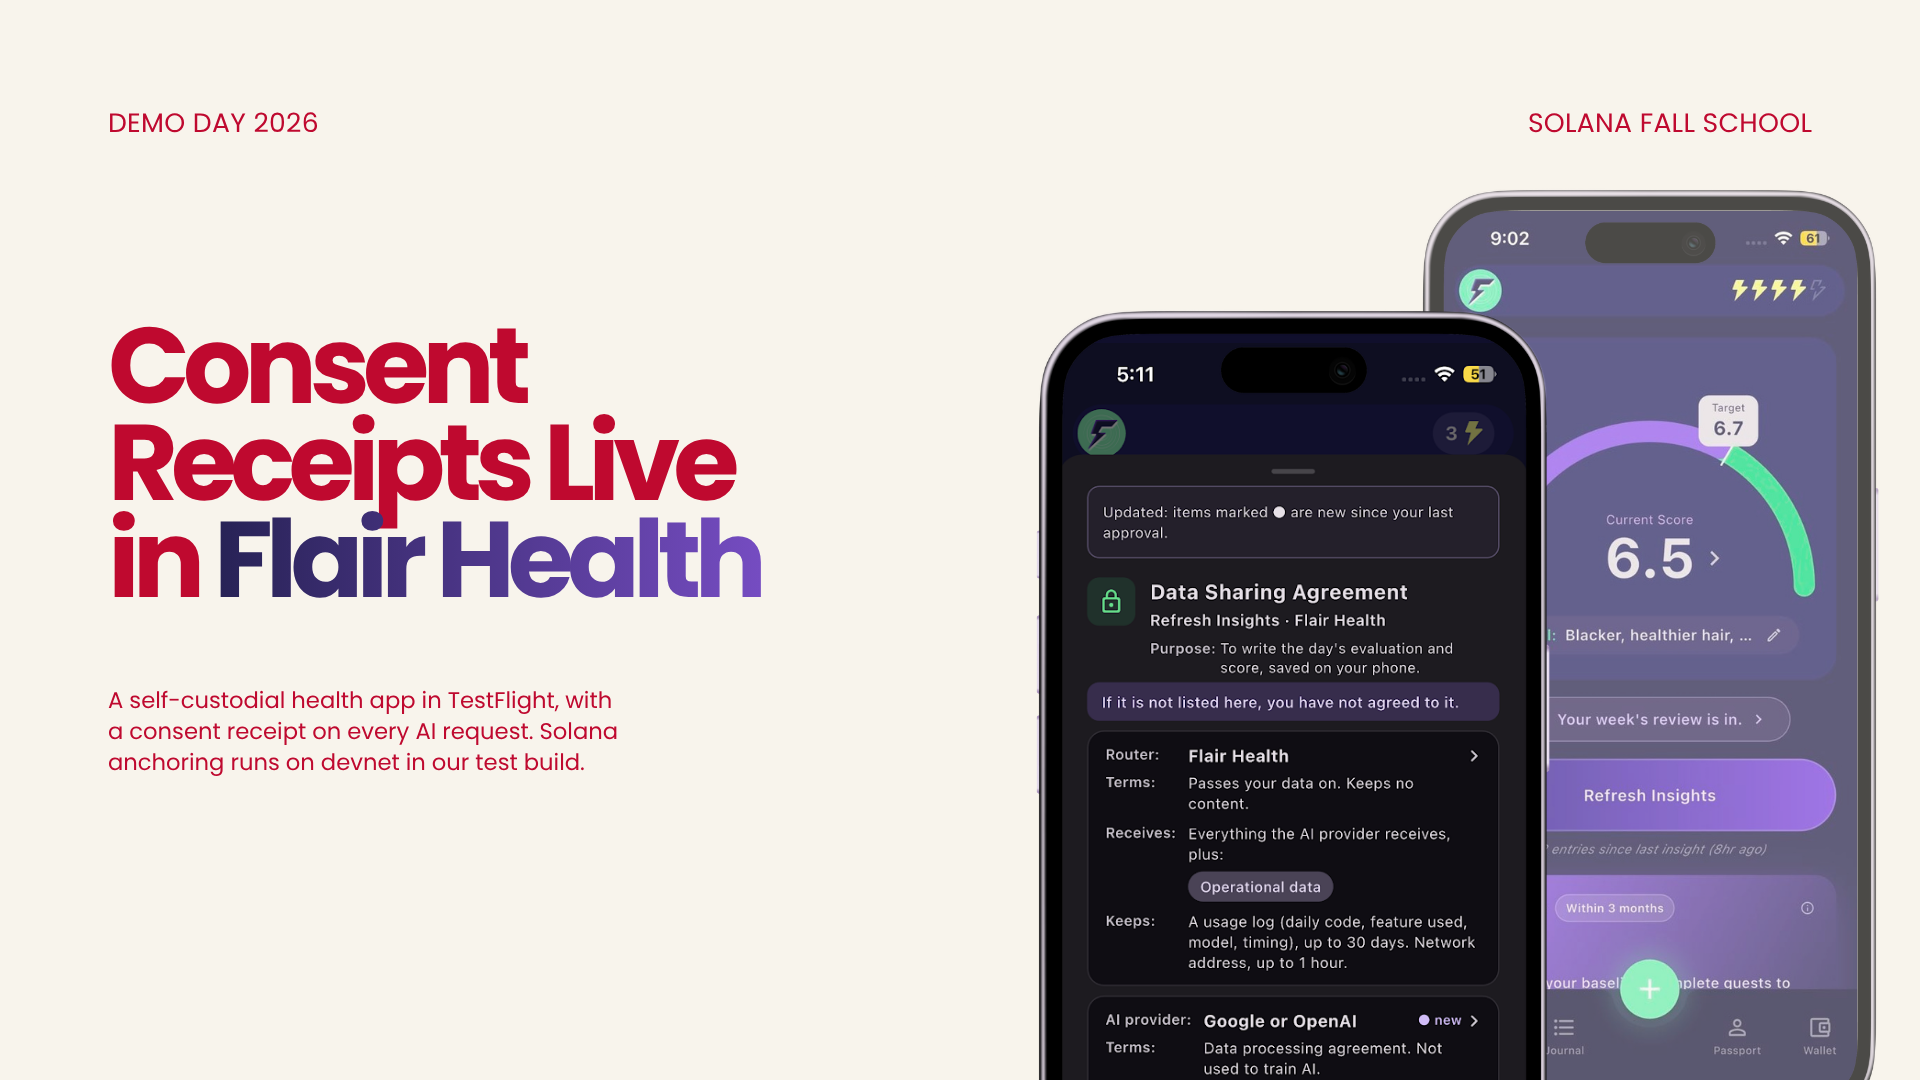
Consent receipts is live in Flair Health build 50, which went out to our TestFlight testers on 24 October. AI requests in it leave a receipt on the phone and anchoring reaches users when we move to Solana’s main network.
Read the full write-up: https://www.regal-pines.com/news-overview/consent-receipts
Give feedback to the team
Your message is private to you and the Consent Receipts team.
Create an account to send feedbackAfter signup, you can write a private message with this update attached.