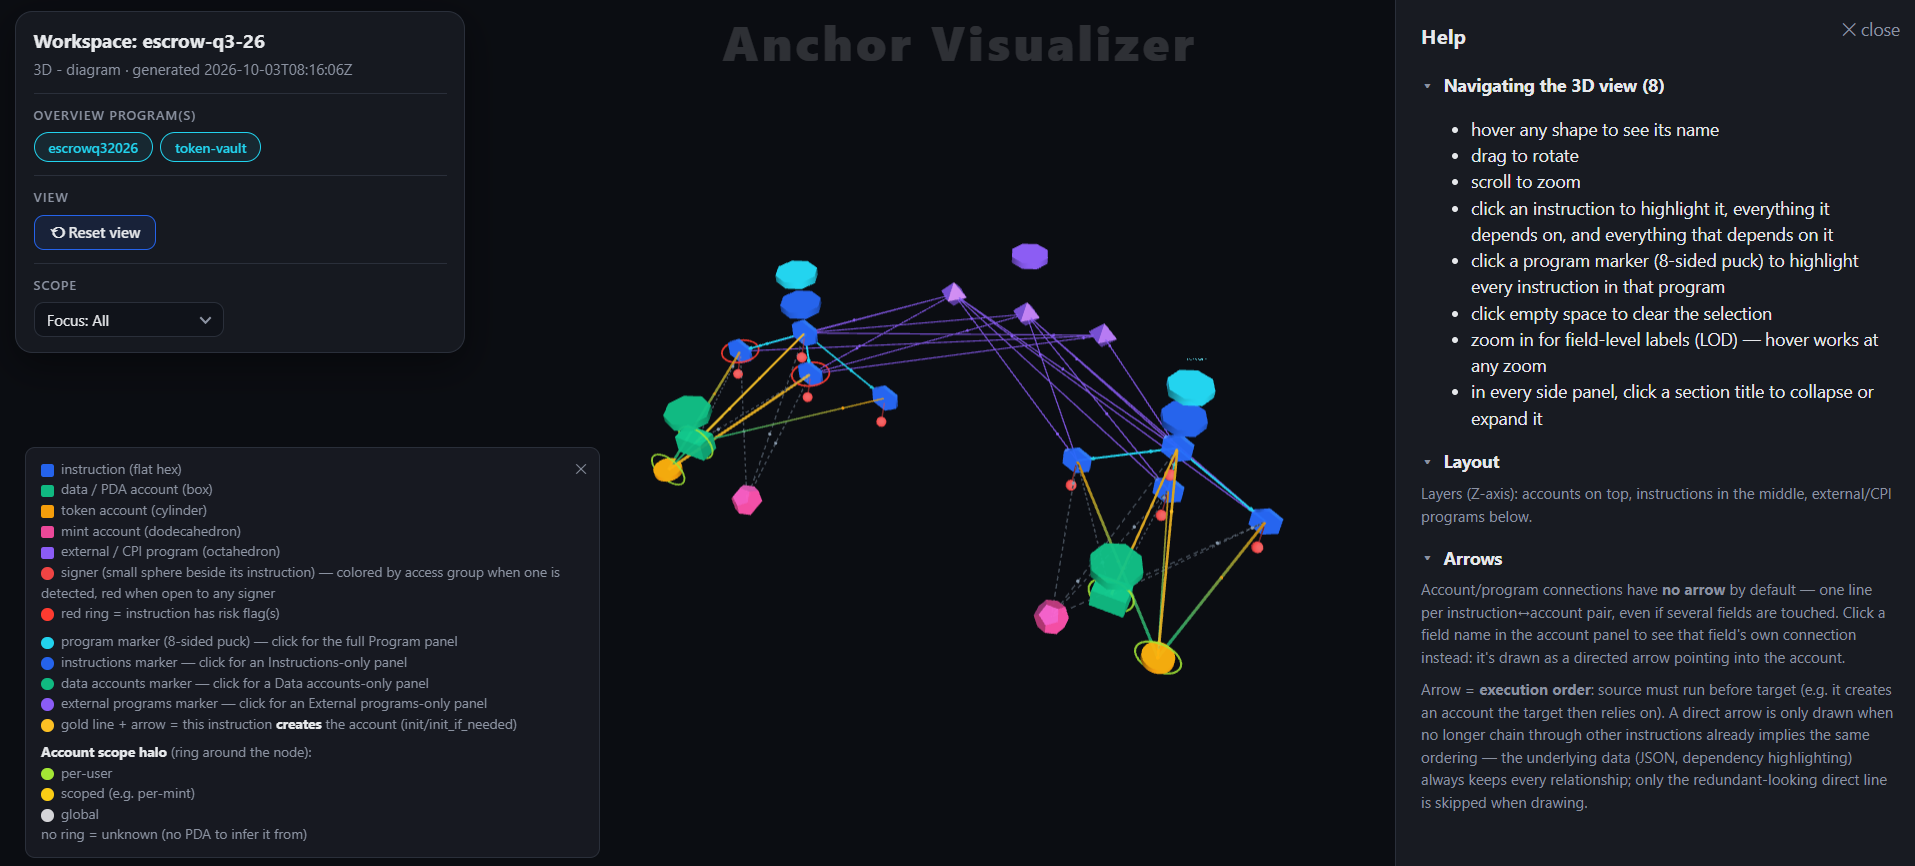
Anchor Visualizer solves this. It is a high-performance static analysis engine built in Rust that reverse-engineers abstract macros into interactive 2D/3D instruction maps, ordered dependency graphs, and precise CPI call paths — with zero deployment required.
We designed the core as a reusable architecture. It can power local tools, run inside a hosted Web Service, embed into a VS Code extension, or integrate straight into automated CI/CD pipelines.
This week, we took the core parser and heavily leveled up its depth, scalability, and security features:
• Standalone Rust Crate: We decoupled the core engine into a reusable Rust crate. This forms the foundation for our upcoming VS Code extension and web dashboards, and lets other security tools plug right in.
• Automated Security Flags: Instead of forcing humans to double-check every line, the engine now automatically scans your code for critical Solana vulnerabilities before deployment. This instantly saves hours of manual auditing and catches catastrophic, multi-million-dollar security holes in seconds.
• Scalable 3D Workspaces: Multi-program architectures now get a "Focus Mode" with smooth camera flights and color-coded objects. Click any object to instantly jump to it and filter the view.
Give feedback to the team
Your message is private to you and the Anchor Visualizer team.
Create an account to send feedbackAfter signup, you can write a private message with this update attached.